Can Your Company Prove a Cyber Incident Happened? The Role of Digital Forensics
A cyber incident can leave a business with more questions than answers.
Who accessed the system? When did they get in? What did they look at? Was any information copied? Did the attacker create another account? Was the incident limited to one computer, or did it reach the wider network?
These questions cannot always be answered by looking at a damaged computer or checking whether files are still available.
This is where Digital Forensics Services UAE businesses use can make a significant difference.
Digital forensics is about examining digital information to understand what happened during a security incident. It can involve computers, servers, email accounts, cloud platforms, network records, mobile devices, and other sources of digital evidence.
For Defense Numerique, the objective is not simply to find suspicious activity. It is to build a reliable picture of the incident that management can understand and act upon.
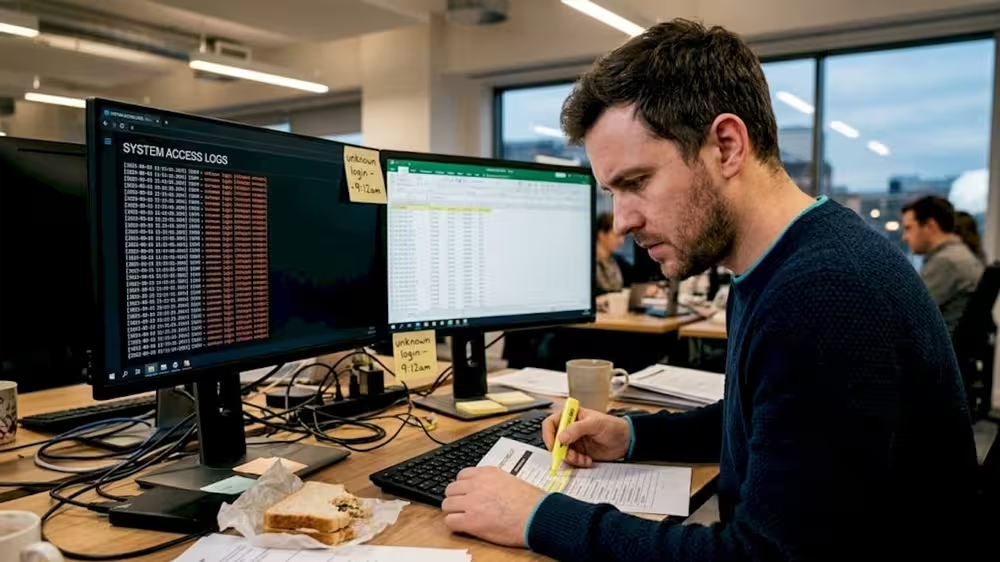
Why Proving What Happened Matters
After a cyber incident, the first priority is usually containment.
That makes sense. A business wants to stop the attacker and get its operations running again.
But there is another question that should not be ignored:
What actually happened?
Suppose an employee’s account was compromised. The company resets the password and continues working. A few days later, management wants to know whether customer information was accessed.
Without the right records, the answer may be difficult to establish.
A proper Digital Forensic Investigation can help reconstruct activity from the evidence that remains. It may identify the first suspicious login, show which systems were accessed, and establish a sequence of events.
This information can be important for management decisions, insurance claims, internal investigations, regulatory discussions, contractual obligations, or legal proceedings.
NIST describes digital forensics as involving the identification, collection, examination, analysis, and reporting of digital evidence while maintaining its integrity and chain of custody.
What Does Digital Evidence Look Like in a Business?
Digital evidence is not necessarily a dramatic file labelled “Hacker Activity.”
It is often hidden among ordinary business records.
A login at an unusual time may become evidence when combined with an unexpected file download. A new administrator account may look harmless until it is connected to a suspicious remote connection.
- Computer and server logs
- Email records
- Authentication activity
- VPN connections
- Firewall logs
- Cloud audit records
- File access history
- Browser activity
- Endpoint security alerts
- Network traffic
- Database activity
- Malware samples
- System memory
- Mobile device information
A single record may not tell the whole story.
The value comes from connecting different pieces.
That is one reason Digital Evidence Investigation requires more than simply opening a log file and searching for unusual words.
Logs, Emails, Endpoints, Network Traffic and Cloud Records
Modern businesses rarely operate from one system.
An employee might use Microsoft 365 or Google Workspace for email, a cloud platform for files, a CRM for customer information, a VPN for remote access, and several SaaS applications for daily work.
An investigation therefore needs to look at the environment as a whole.
Log Records
Logs can show when users logged in, what systems they accessed, and what changes were made.
Email Records
Email evidence can help identify phishing messages, suspicious forwarding rules, unusual sign-ins, or attempts to steal credentials.
Endpoint Evidence
Laptops and desktops can contain useful information about programs executed, files accessed, removable devices, and other activity.
Network Evidence
Network records may help identify communication between an affected system and an external destination.
Cloud Evidence
Cloud audit logs can reveal changes to accounts, permissions, storage, applications, and configurations.
NIST’s guidance on forensic techniques specifically identifies files, operating systems, network traffic, and applications as potential sources of forensic data.
At Defense Numerique, these sources can be examined together to develop a clearer understanding of an incident.
Establishing the Timeline of an Attack
One of the most useful outcomes of Cybersecurity Forensics UAE work is a reliable timeline.
A timeline turns scattered technical records into a sequence.
For example:
8:42 AM: An employee receives a suspicious email.
8:51 AM: The employee’s credentials are used from an unusual location.
9:04 AM: A new login occurs against a cloud application.
9:17 AM: Privileged access is obtained.
9:36 AM: Several files are accessed.
10:12 AM: An unusual external connection is detected.
10:28 AM: Security staff discover the incident.
Individually, these events may not tell management much.
Together, they can show how the incident developed.
The timeline can also reveal gaps in detection. Perhaps the first suspicious login occurred several hours before anyone noticed the problem.
That information can guide future security improvements.
Identifying the Initial Point of Compromise
Finding out where the attacker first entered is one of the most important parts of an investigation.
It could be:
- A stolen password
- A phishing email
- An exposed remote service
- An unpatched application
- A compromised third-party account
- A malicious file
- A vulnerable internet-facing system
Finding the entry point matters because closing the wrong door does not stop the attacker from coming back through another one.
For example, changing one employee’s password may not be enough if the attacker also created a hidden account or obtained another set of credentials.
A Digital Forensic Investigation helps investigators work backwards through available evidence rather than relying entirely on assumptions.
Understanding What the Attacker Did After Getting In
Getting inside the network is only the beginning.
The next question is what happened after access was obtained.
Investigators may look for signs of:
- Privilege escalation
- Account creation
- Lateral movement
- File access
- Data collection
- Security-control changes
- Remote access
- Malware execution
- Data transfer
This is where a Digital Evidence Investigation can help establish the difference between suspected access and confirmed activity.
For a business, that distinction matters.
There is a significant difference between saying:
“We think customer data may have been accessed.”
and:
“We identified access to the customer database from a compromised account during a defined period.”
The second statement is based on evidence.
Evidence Preservation and Chain of Custody
Digital information can be changed very easily.
Restarting a computer can remove information stored in memory. Logs may be overwritten. Files can be modified. A system administrator working on a compromised server may unintentionally change important evidence.
This does not mean businesses should stop all recovery work.
It means investigation and recovery need to be coordinated.
Evidence should be collected and handled in a way that preserves its integrity. A record should also be maintained showing who collected it, when it was collected, where it was stored, and who subsequently handled it.
This is known as maintaining a chain of custody.
NIST guidance emphasizes documenting the handling of evidence and maintaining records of who handled it, when it was handled, and where it was stored.
For Digital Forensics Services UAE businesses require after a serious incident, this process is particularly important when the findings may later need to be reviewed by legal, compliance, insurance, or other external parties.
When Internal IT Investigation Is Not Enough
Internal IT teams are often the first people to respond to a security incident.
They know the company’s systems. They know which servers are important. They understand how applications are configured.
But incident investigation can require specialist tools, experience, and dedicated time.
The situation becomes more difficult when:
- The incident affects multiple systems
- Administrator credentials may be compromised
- Sensitive information may have been accessed
- Malware is involved
- The attacker remained inside the environment for an extended period
- There is suspected insider activity
- Legal or regulatory questions may follow
- The organization needs an independent investigation
Trying to investigate everything while simultaneously restoring business operations can create conflicts.
A specialist Digital Forensics Company UAE businesses work with can provide dedicated investigation while internal teams focus on keeping the business functioning.
How Digital Forensics Supports Management and Legal Teams
Technical teams need technical answers.
Management often needs different answers.
They want to know:
What happened?
How serious is it?
Which systems were affected?
Was sensitive information accessed?
When did the incident begin?
What needs to be fixed?
A good forensic investigation should turn technical findings into information that decision-makers can understand.
For legal and compliance teams, the investigation may provide a documented basis for assessing obligations and deciding what additional action is necessary.
This is especially important when personal information or confidential business data is involved. UAE businesses should also consider the applicable data protection requirements for their activities. The UAE’s Personal Data Protection Law establishes a framework for protecting personal data and defines obligations around its processing and protection.
Defense Numerique approaches forensic work with this wider business context in mind.
The goal is not to overwhelm management with hundreds of technical log entries.
The goal is to explain what the evidence means.
What a Digital Forensic Report Should Tell You
A useful report should answer the questions that matter.
At Defense Numerique, a practical forensic report can be structured around:
Executive Summary
A concise explanation of the incident, its impact, and the most important conclusions.
Technical Findings
The systems, accounts, devices, activities, and evidence identified during the investigation.
Analysis and Details
The investigation timeline, suspected entry point, attacker activity, affected systems, and supporting evidence.
Recommendations
Actions required to address weaknesses, improve monitoring, strengthen access controls, and reduce the likelihood of another incident.
This approach allows both technical and non-technical stakeholders to understand the outcome.
NIST’s forensic guidance also describes reporting as a core part of the forensic process, alongside identifying, acquiring, protecting, processing, and analyzing data.
Why Defense Numerique for Digital Forensics?
A cyber incident creates uncertainty.
Defense Numerique helps businesses replace that uncertainty with evidence.
Our Digital Forensics Services UAE approach can support organizations investigating suspicious activity, unauthorized access, malware incidents, data exposure, insider concerns, and other security events.
Our Digital Forensic Investigation process focuses on preserving relevant evidence, establishing timelines, identifying affected systems, and translating technical findings into practical business recommendations.
Final Thought
A business may be able to restore a server without knowing exactly what happened.
It may be able to reset passwords without knowing whether an attacker accessed sensitive information.
But recovery without understanding can leave important questions unanswered.
Digital forensics helps close that gap.
For Digital Forensics Services UAE businesses, the objective is not simply to find evidence. It is to understand the story that the evidence tells.
At Defense Numerique, we believe that knowing what happened is the foundation for knowing what to fix next.
Because after a cyber incident, “we think” is rarely good enough.
Evidence gives you the confidence to act.
FAQ's
01.
A Digital Forensic Investigation is a structured examination of electronic evidence to determine what happened during a suspected security incident. Investigators may examine computers, servers, emails, cloud systems, network records, and other digital sources. The objective is to establish facts such as how access occurred, what activity followed, which systems were affected, and whether information may have been accessed or transferred.
02.
A business should consider Digital Forensics Services UAE providers when it suspects unauthorized access, data theft, malware activity, compromised administrator accounts, insider activity, or a serious cyber incident. Specialist support is particularly useful when the organization needs a reliable incident timeline, evidence preservation, independent investigation, or technical findings that may need to be reviewed by management, legal teams, insurers, or regulators.
03.
Normal IT troubleshooting focuses mainly on restoring a system or fixing a technical problem. A Digital Evidence Investigation focuses on determining what happened and preserving information that can support that conclusion. Instead of simply removing malware or rebuilding a computer, investigators examine available evidence to understand the attack path, user activity, affected systems, and potential data exposure.
04.
Digital forensics can examine many sources, including computers, servers, emails, authentication records, cloud audit logs, VPN activity, firewall records, network traffic, mobile devices, databases, and endpoint security information. The appropriate evidence depends on the incident. Defense Numerique can help determine which sources are relevant instead of collecting information without a clear investigative purpose.
05.
A Digital Forensics Company UAE can investigate how the breach occurred, identify compromised accounts and systems, establish an incident timeline, preserve relevant evidence, and assess available indicators of data access or transfer. The resulting findings can help management understand the incident and give legal, compliance, and security teams a stronger factual basis for deciding what should happen next.
06.
Cybersecurity Forensics UAE work complements incident response by adding investigation to immediate containment and recovery. Incident responders focus on stopping the threat and reducing damage, while forensic specialists examine evidence to determine how the compromise occurred and what the attacker did. Defense Numerique can coordinate these activities so recovery actions do not unnecessarily interfere with the investigation.
07.
There is no fixed timeframe because every investigation is different. A small incident involving one endpoint may be completed relatively quickly, while a larger investigation involving cloud platforms, multiple servers, privileged accounts, or suspected data theft can take considerably longer. Defense Numerique first establishes the scope and available evidence before determining the appropriate investigation approach.
Tags :
Blog
Follow Us :
Related Post