The Hidden Attack Surface in UAE Business Networks: Forgotten Assets and Shadow IT
A company may know the servers it purchased, the applications its IT team manages, and the cloud platforms approved by management. But that does not always mean it knows everything connected to its business environment.
An old server may still be online.
A test website may still be publicly accessible.
An employee may have created a SaaS account without informing IT.
An unused domain may still point somewhere.
An old API key may still work.
These overlooked assets can become part of the Attack Surface in UAE Business environments.
NIST defines an attack surface as the points where an attacker can try to enter a system, cause an effect, or extract data.
For UAE businesses that are expanding their cloud infrastructure, digital services, remote access and third-party platforms, knowing what is exposed is becoming just as important as protecting what is already known.
The challenge is simple:
You cannot properly secure an asset that your security team does not know exists.
What Is an Unknown or Forgotten Digital Asset?
An unknown or forgotten digital asset is a system, service, application, domain, account, device or other technology resource that is no longer properly tracked or managed by the organization.
It does not necessarily mean that someone intentionally hid it.
In many cases, these assets are created as part of normal business activity.
For example:
- A developer creates a temporary test server.
- A marketing team launches a campaign website.
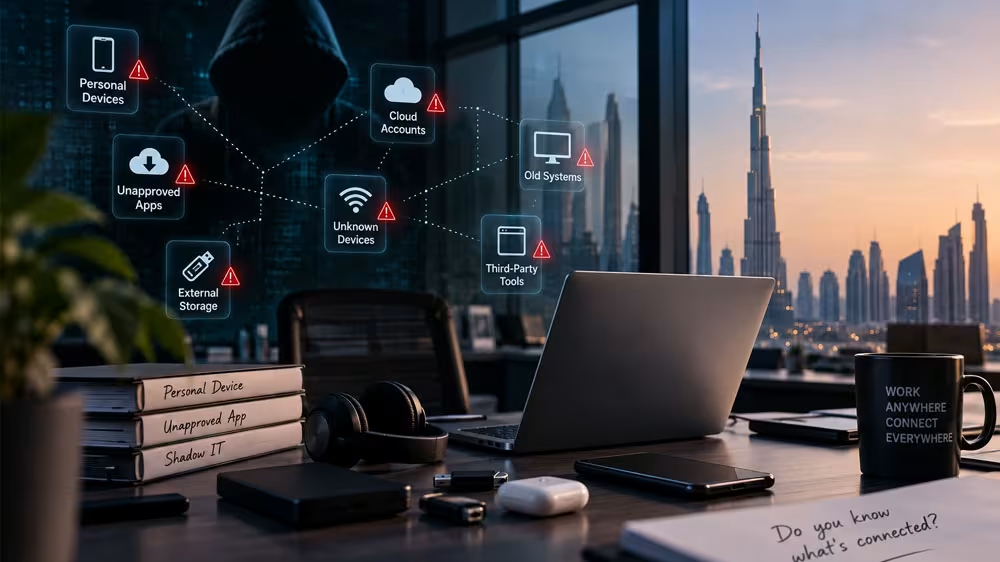
- An employee signs up for a cloud application.
- A contractor creates a remote-access account.
- An old application is replaced but its server remains active.
- A company acquires another business and inherits systems nobody has fully reviewed.
Over time, these assets can disappear from internal documentation while remaining technically accessible.
This creates a visibility problem.
NIST emphasizes that organizations need accurate asset inventories to understand what assets they have, where they are, and how they are being used.
Why Forgotten Assets Become Part of the Attack Surface in UAE Business Environments
The attack surface of a business is not fixed.
It changes when the business:
- Launches a new website
- Adds a cloud service
- Opens a new office
- Connects a third-party platform
- Deploys a mobile application
- Creates a remote-access service
- Acquires another company
- Changes DNS records
- Adds APIs
- Moves workloads between cloud environments
The problem is that security documentation may not change at the same speed.
An asset can therefore remain online even after the business has stopped actively using it.
From an attacker’s perspective, an overlooked system may still be useful.
From the company’s perspective, it may not even appear on the security team’s list.
That gap is where External Attack Surface UAE concerns begin.
Old Servers and Unused Domains
Old infrastructure is one of the easiest things for businesses to forget.
An organization may replace an application but leave the underlying server running because someone still believes it may be needed later.
Similarly, an old domain or subdomain may remain active after a project has ended.
Consider a company that previously used:
old-portal.company-domain
The portal is no longer part of normal operations, but the server behind it remains connected to the internet.
Nobody actively monitors it.
Nobody checks whether its software is still supported.
Nobody remembers who has administrator access.
The business may have moved on, but the system has not.
This is why asset lifecycle management matters.
NIST’s Cybersecurity Framework implementation guidance specifically recommends managing systems, hardware, software and services throughout their life cycles and periodically identifying redundant assets that unnecessarily increase attack surface.
What businesses should review
For older systems, security teams should know:
- Who owns the asset?
- Is it still required?
- Is it internet-facing?
- What software is running?
- Is it still receiving security updates?
- Who has access?
- Does it connect to other business systems?
- Can it be safely removed?
If nobody can answer these questions, the asset deserves attention.
Test Environments Accidentally Exposed to the Internet
Development and testing environments are useful because teams need somewhere to build and test new applications.
The problem begins when a test environment becomes publicly accessible without the same security controls applied to production.
A developer may need a temporary environment to test a new application.
The project finishes.
The test environment remains online.
The application may contain old code, sample data, debug configurations or credentials that were never intended for public access.
This does not mean every test environment is insecure.
The issue is unnecessary exposure combined with weak ownership and poor visibility.
CISA recommends that organizations first identify which assets are accessible from the internet, determine which ones actually need that exposure, and reduce or restrict unnecessary exposure. It also recommends routinely reviewing internet-accessible assets as environments change.
For UAE businesses, this should be part of the normal process when applications move from development to production.
Shadow IT and Unauthorized SaaS Applications
Shadow IT is not necessarily a malicious activity.
It often starts with an employee trying to solve a business problem quickly.
For example, a team may start using an online service to:
- Share documents
- Manage projects
- Transfer large files
- Automate a workflow
- Analyse data
- Communicate with external partners
- Store business information
The employee may not realize that the service creates a new security and data-management concern.
The IT team may not know the account exists.
This is the problem behind Shadow IT Cybersecurity.
Why Shadow IT can be difficult to manage
A SaaS application may involve:
- Business documents
- Customer information
- Employee information
- Company credentials
- API integrations
- Third-party users
- Automated data transfers
If the security team does not know the service is being used, it may not be included in security reviews, access reviews or incident-response planning.
NIST’s current incident-response guidance specifically calls for current inventories of software, services and systems and identifies those inventories as useful for identifying shadow IT.
A better approach
Businesses should not treat every unauthorized application as an employee misconduct issue.
A more practical approach is to ask:
Why did the employee need it?
If the business need is legitimate, security and IT teams can determine whether the application can be approved, controlled or replaced with an approved alternative.
Forgotten Cloud Accounts and API Keys
Cloud environments can grow quickly.
One project may use several cloud accounts, storage services, databases, applications and APIs.
When a project ends, the infrastructure may not be fully removed.
An old cloud account may still exist.
An unused storage resource may remain configured.
An API key may have been created for testing and never properly retired.
These are not necessarily visible from a traditional office-network security review.
Cloud environments require their own inventory and ownership controls.
For each cloud account or resource, businesses should be able to answer:
- Who owns it?
- What business purpose does it serve?
- What data does it contain?
- Who can access it?
- Is it publicly accessible?
- Which applications depend on it?
- Are unused credentials or keys still active?
The objective is not to eliminate cloud services.
It is to ensure that cloud resources remain known, owned and appropriately protected.
Exposed Remote Access Services
Remote access is now a normal requirement for many organizations.
Employees, administrators, vendors and contractors may need to connect to business systems from outside the office.
But every externally accessible remote service creates another point that needs to be managed.
Examples can include:
- Remote administration portals
- VPN services
- Remote desktop infrastructure
- Vendor access platforms
- Cloud management interfaces
- Remote support tools
The security question is not simply:
“Do we use remote access?”
It is:
“Which remote-access services are exposed, who uses them, and are they still necessary?”
CISA recommends reviewing internet-accessible assets, restricting exposure that is not operationally necessary, keeping exposed systems updated, using stronger authentication controls where possible, and continuously reassessing internet exposure.
For organizations with contractors or third-party support teams, ownership and access reviews become especially important.
Why Attackers Look for Overlooked Assets
Attackers do not need to find the most obvious route into a company.
An overlooked system can sometimes provide an alternative path.
A forgotten application may use outdated software.
A test environment may have weaker security controls.
A cloud account may have an unknown administrator.
A remote-access service may belong to a system nobody actively monitors.
An old domain may point to infrastructure that has not been reviewed for years.
The key issue is not that forgotten assets are automatically vulnerable.
The issue is that unknown assets are difficult to assess properly.
NIST has repeatedly emphasized the importance of asset visibility. Its current work on OT asset management describes asset inventory as foundational to understanding cybersecurity risk and notes that organizations cannot effectively defend environments they cannot see.
How to Build an External Attack-Surface Inventory
Building an External Attack Surface UAE inventory does not have to start with an expensive technology project.
The first step is to establish ownership and visibility.
1. Start With Known Business Assets
Create a list of:
- Official domains
- Subdomains
- Public IP addresses
- Cloud environments
- Public applications
- Remote-access services
- APIs
- Internet-facing infrastructure
Then identify who owns each asset.
2. Compare the List With External Visibility
The next question is:
What can be seen from outside the organization?
External assessment can reveal systems and services that may not appear in an internal asset register.
CISA’s exposure-reduction guidance recommends identifying internet-accessible assets and regularly reviewing them as the environment changes.
3. Identify Unknown Assets
For every discovered asset, ask:
Do we own this?
Who is responsible for it?
Why is it exposed?
Is it still required?
Does it contain or connect to business data?
Unknown ownership should be treated as a security-management issue.
4. Classify the Risk
Not every exposed asset represents the same level of risk.
Consider:
- Internet exposure
- Business importance
- Data sensitivity
- Authentication controls
- Software condition
- Connectivity to other systems
- Third-party access
This helps security teams focus their attention.
5. Remove What Is No Longer Needed
If an asset is unnecessary, the safest solution may be to remove it or restrict its exposure.
Reducing unnecessary assets can reduce the organization’s attack surface.
6. Make Discovery Continuous
An inventory created once can become outdated.
New applications, cloud services, domains and remote-access systems can appear as the business changes.
Asset discovery should therefore be part of an ongoing security process rather than a one-time project.
How VAPT Can Identify Overlooked Exposure
Asset discovery tells you what is exposed.
Vulnerability assessment helps determine what weaknesses may exist.
Penetration testing can provide deeper validation within an authorized scope.
This is where Vulnerability Assessment UAE becomes relevant.
A VAPT engagement can help organizations examine known and discovered assets for security weaknesses and determine which findings require further attention.
For example, a previously unknown internet-facing application may be discovered during an external assessment.
The next questions are:
- What technology is it using?
- Is it still supported?
- Is authentication configured correctly?
- Does it expose sensitive functionality?
- Does it connect to internal systems?
- Are there weaknesses that require remediation?
The objective is not simply to generate another vulnerability list.
It is to connect asset visibility with actual security risk.
Defense Numerique provides VAPT and penetration testing services for organizations that need to assess their security exposure and identify weaknesses within an agreed scope.
You can explore the VAPT Services provided by Defense Numerique or review its Penetration Testing service to understand how deeper security testing can support external and internal security assessments.
UAE Businesses Should Treat Asset Visibility as a Business Issue
For a growing UAE company, the technology environment can change quickly.
New offices are opened.
Cloud platforms are introduced.
Employees work remotely.
Third-party vendors receive access.
Applications are launched.
Companies merge or acquire other businesses.
Every change can add another asset.
At the same time, UAE organizations handling personal information need to consider applicable data-protection requirements. The UAE Government identifies Federal Decree-Law No. 45 of 2021 concerning the Protection of Personal Data among the country’s cyber and data-protection laws.
That does not mean every forgotten asset automatically creates a regulatory violation.
It does mean organizations should understand where relevant systems and data exist and who has access to them.
Good asset visibility supports better decisions across security, IT, compliance and management.
What Management Should Ask About the Attack Surface in UAE Business
Security teams can start with a few practical questions:
Do we know every internet-facing asset?
If the answer is uncertain, external asset discovery may be required.
Do we know who owns each asset?
An asset without a clear owner can easily become neglected.
Are old systems still exposed?
Retired applications and infrastructure should be reviewed before they become forgotten entry points.
Are employees using unapproved SaaS platforms?
Shadow IT should be identified and managed rather than simply ignored.
Do we know which cloud accounts and API credentials still exist?
Unused cloud resources and credentials should have an owner and a defined business purpose.
Are remote-access services still required?
Every externally accessible service should have a clear reason for being exposed and appropriate security controls.
Are new assets automatically added to security reviews?
Security needs to keep up with business changes.
How Defense Numerique Can Help
Understanding the Attack Surface in UAE Business environments starts with visibility.
Defense Numerique provides cybersecurity services that can help organizations identify weaknesses and improve their understanding of security exposure.
For businesses concerned about forgotten internet-facing systems, exposed applications, cloud resources or other security weaknesses, VAPT and Penetration Testing can form part of a broader assessment strategy.
The appropriate scope depends on the organization’s infrastructure, business requirements and security objectives.
The goal is simple:
Know what you have.
Know what is exposed.
Understand what could create risk.
Fix what matters.
FAQ's
01.
The attack surface in UAE business environments is the collection of systems, applications, services, devices, accounts and other points that could potentially be targeted or accessed by an attacker. It can include public websites, cloud resources, remote-access services, APIs, domains and third-party connections.
02.
Shadow IT Cybersecurity refers to the security risks created when employees or teams use applications, cloud services, devices or platforms without the organization's normal IT approval or visibility. The concern is not simply unauthorized software; it is that security, access, data and monitoring controls may not cover those services.
03.
Forgotten assets can become a cybersecurity risk because they may remain connected to business networks or the internet without regular security reviews. An old server, test application or cloud resource may have outdated software, unclear ownership or unnecessary access, making it harder for the organization to identify and manage potential exposure.
04.
Vulnerability Assessment UAE services can help organizations identify security weaknesses across systems and applications within an agreed scope. When combined with asset discovery, the assessment can provide better visibility into exposed systems and help security teams prioritize weaknesses based on the asset, exposure, potential impact and business importance.
05.
An external attack surface consists of systems and services that can be reached or observed from outside an organization's environment. Examples may include public websites, domains, APIs, cloud services, VPN gateways and other internet-facing infrastructure. Maintaining visibility over these assets helps organizations identify unnecessary exposure and security weaknesses.
06.
There is no single schedule that applies to every organization. Businesses should review external exposure regularly and whenever significant changes occur, such as launching applications, adding cloud services, acquiring companies, changing remote access or retiring infrastructure. Organizations with rapidly changing environments may need more continuous monitoring and discovery.
Tags :
Blog
Follow Us :
Related Post